Odd Bits / Builder kits
Supabase Safety Kit
Supabase projects most often leak data through a few repeat mistakes: a table with Row Level Security off, a policy that lets every row through, a function that runs with its owner's rights. This kit has read-only SQL that looks for those patterns, a way to switch a route off in an emergency, and checklists for migrations and backups. A checklist, not a security guarantee.
- What you get
- Eight read-only SQL checks, tested against three made-up schemas
- A tested kill-switch guard to turn a route off in an emergency
- Checklists for RLS review, migrations, backups and before launch
- Works with
- SupabasePostgres 15+Node 22.6+ (kill-switch)
- Version
- v1.0, updated 2026-10-19
Email for an invoice: $9.99Paid by invoice for now. Files arrive by email once it clears.
How you get it: email me. I send a USD invoice through Wise; when it clears, the files come by email as a zip, within one working day. A hosted checkout may replace the invoice later.
What's inside
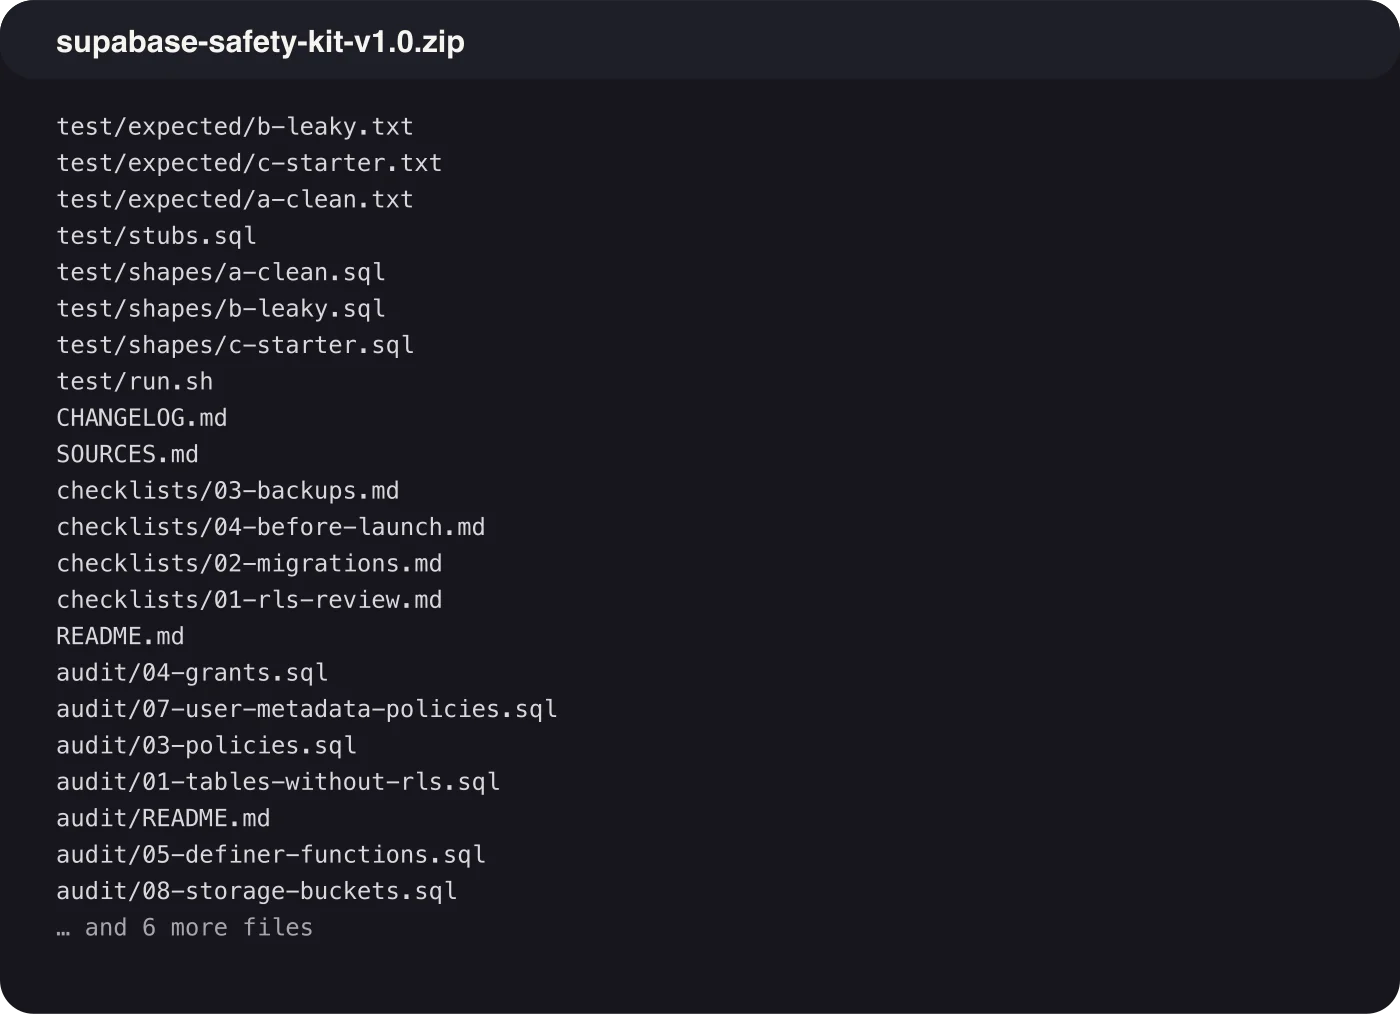
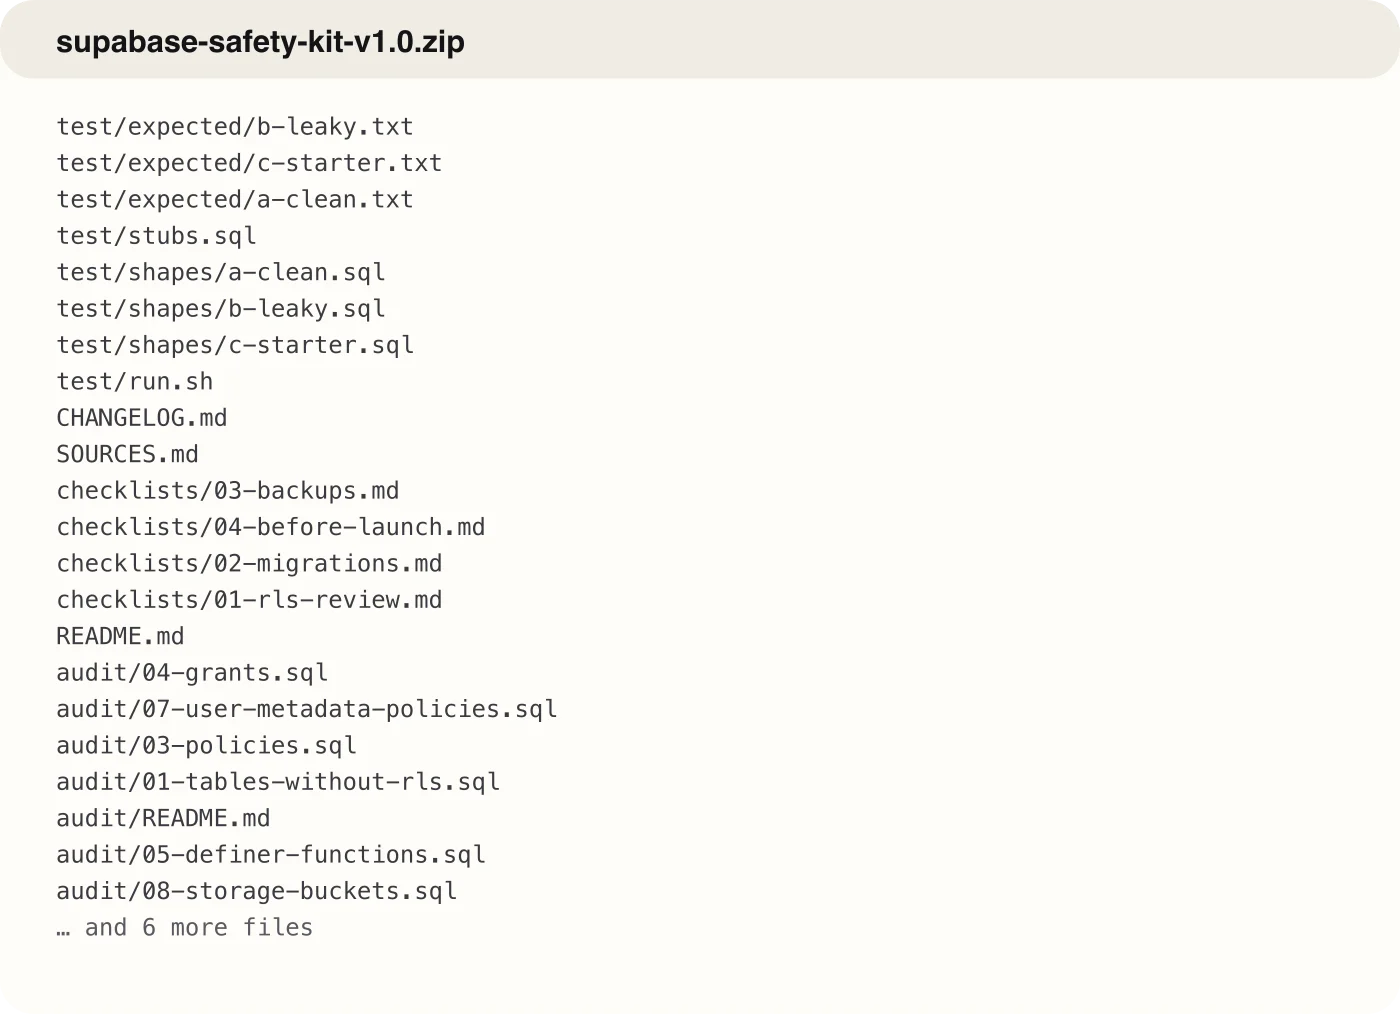
- audit/01 to 07: read-only SQL queries that read the system catalogs only. Each returns no rows when it finds nothing
- audit/08: the same idea for Storage buckets, if you use Storage
- audit/ALL.sql: files 01 to 07 in one file for psql, and an audit/README on how to run and read them
- killswitch/: an environment flag that turns a route (or everything) off, with a guard (guard.ts) and 7 tests
- checklists/: RLS review, migrations, backups and restores, and a before-launch list
- test/: the queries run against three made-up schemas in a throwaway local Postgres and compared with what we expect
- SOURCES.md: each rule that comes from Supabase’s or Postgres’s own pages, with the link and the date I read it
What the checks look for
- Tables in an exposed schema with Row Level Security off
- RLS switched on with no policy (locked for everyone: safe, but usually unfinished)
- Policies that let every row through, and every policy that applies to the anonymous role
- truncate, references and trigger privileges held by the anon or authenticated roles
- security definer functions with no pinned search_path, or that anon can call
- Views that can sidestep RLS, and materialized views the API roles can read
- Policies that read user_metadata, which signed-in users can edit
- Public Storage buckets that can also be listed
Who it's for
Developers and small teams about to launch, or already running, a project on Supabase who want a quick, repeatable pass over the common mistakes before a person reviews the rest.
What it never does
- Promise your project is secure. It is a checklist: a clean result means these patterns were not found, nothing more
- Read your data. It prints object names, policy text and privileges, which can still be sensitive, so do not paste the output into a public place
- Check your app code, API keys, Auth settings, rate limits or network restrictions
- Tell you a policy is correct. A policy like auth.uid() = owner passes every check here and can still be the wrong rule for your app
- Replace Supabase’s own database linter (Advisors). Run theirs as well
- Come from, or claim any link to, Supabase. It is not affiliated with or endorsed by Supabase
Questions
Is this a security audit?
No. It looks for specific, common patterns. For anything that matters (money, health, children’s data), get a person who does security to look.
Was it tested on a real Supabase project?
No. It was tested on Postgres 15.16 on a local machine, with plain stand-ins for the Supabase roles and the auth and storage tables. You can run test/run.sh yourself (it needs initdb, pg_ctl and psql).
Do the queries change anything?
No. They are read-only and read the system catalogs. Read each file before you run it, as with any SQL you did not write.
Which Postgres versions?
Postgres 15 or newer, because security_invoker views need it.
What does the kill-switch need?
Node 22.6 or newer to run its tests. The guard itself is a small TypeScript file you read and adapt.
Can I use it for clients?
Yes. Use and modify it for your own and your clients’ projects. Do not resell or republish the kit as it is.
Will it be updated?
I’ll email fixes to buyers. No schedule is promised.